
3.0 API Testing
API testing that proves reality against the spec
Routebase builds API testing on your OpenAPI contract, so test suites, security scans, and CI automation all enforce the same spec.
14-day Pro trial — no credit card required.
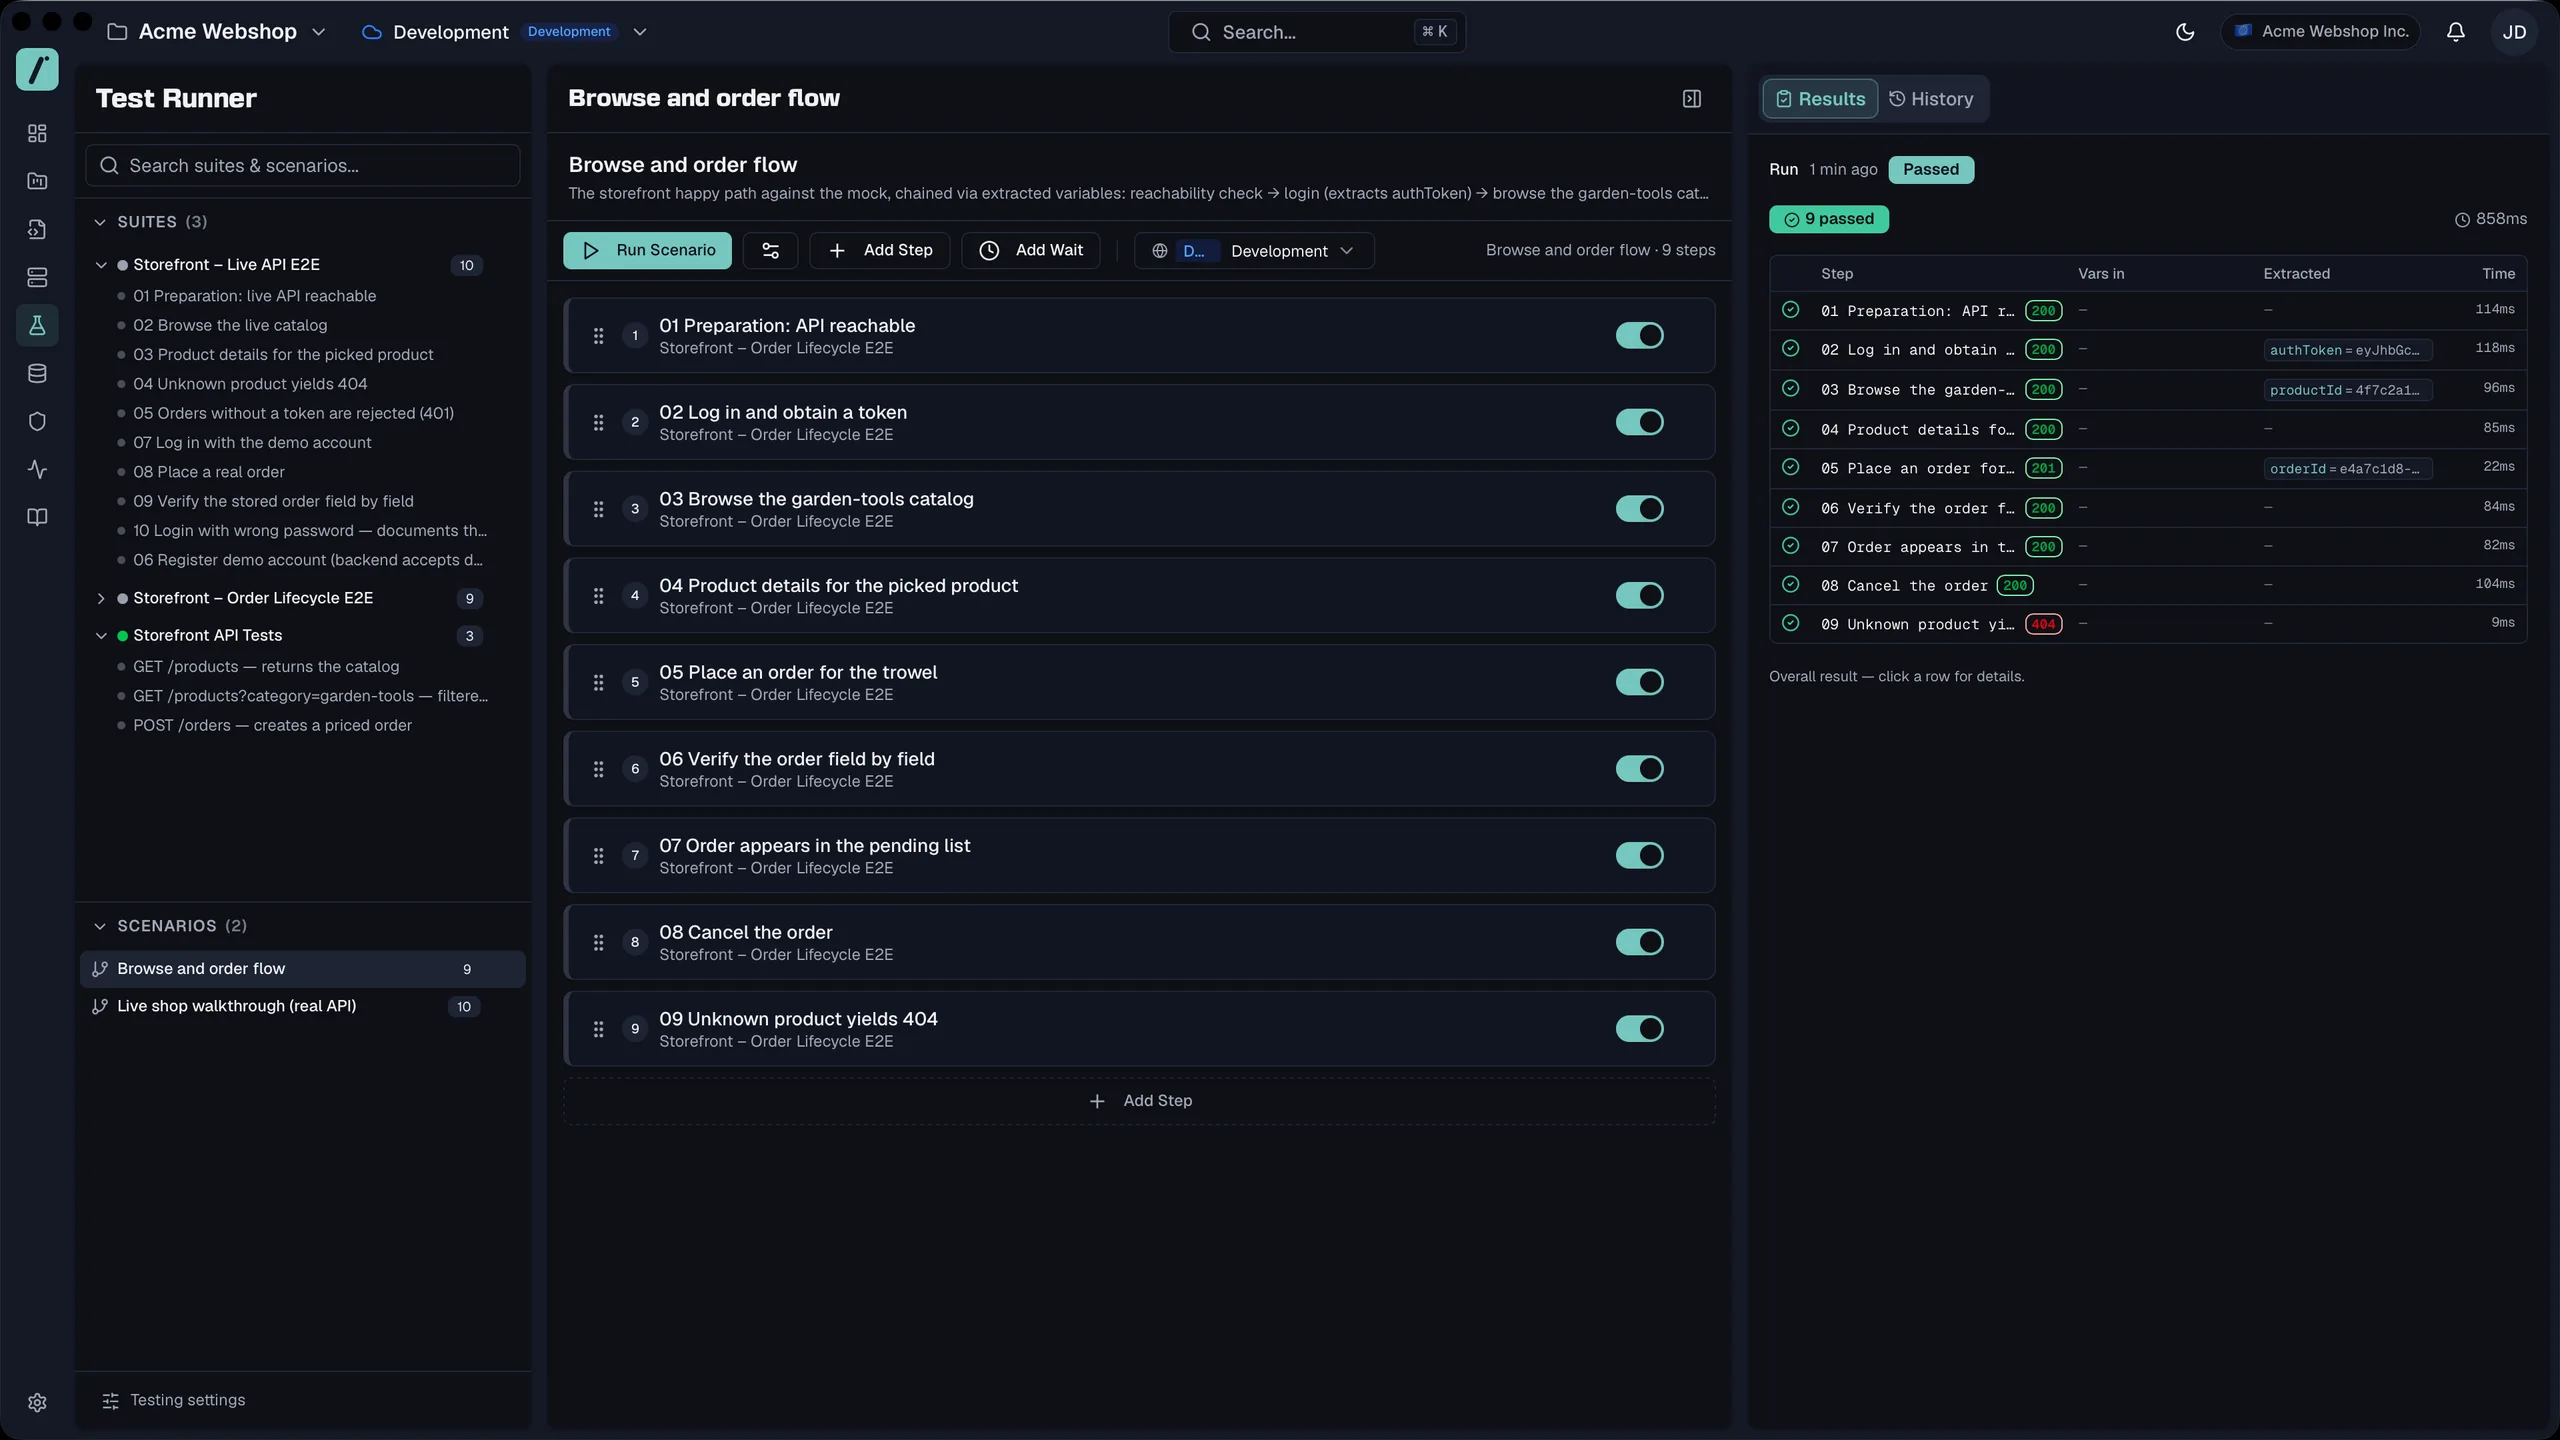
API testing breaks down when the tests live in scripts that nobody updates, so they keep passing while the API quietly changes underneath them. Routebase treats your OpenAPI spec as the contract to enforce, so API tests are declarative suites of chained requests with assertions on status, headers, body, JSON paths, latency, and schema. The same suite runs against staging and production with ten auth schemes resolved per environment, and fixtures, seeds, and snapshots put the API in a known state before every run. Security is part of API testing as well, with OWASP API Top 10 scans and multi-identity personas beside the functional suites. From there, the CLI, cron schedules, and signed webhooks run the suites where your pipeline already lives.
API test suites that assert everything
Suites of chained requests — assert on status, JSON paths, headers, body, latency, and schema with 10 operators.
- 6 assertion types with 10 operators, drag-and-drop suites
- Chained requests: extract values, reuse them downstream
- Pre-request and post-response JavaScript
Auth like production
Ten auth schemes resolved per environment — run the same suite against staging and prod.
- OAuth2, Bearer, API Key, JWT, AWS SigV4, and more
- Environment variables in requests and assertions
Test data, managed
Fixtures, seeds, and snapshots put the API in a known state before every run.
- Fixtures with per-suite scope control
- Pre/post-run seeds with loops and captures
- Logical snapshots restore known state
Security is a test, too
OWASP API Top 10 scanning with multi-identity personas, finding triage, and a security score.
- 13 scanners: BOLA, broken auth, SSRF, fuzzing, and more
- Personas for multi-identity access testing
- Triage workflow with audit trail and score dashboard
API testing in your pipeline
CLI for CI, API triggers, schedules, and signed webhooks — testing that fits your pipeline.
- CLI runner with CI exit codes
- Cron schedules and API-key triggers
- HMAC-signed webhooks on completion
Frequently asked questions
Do I need an OpenAPI spec for API testing in Routebase?
No. A test case is a plain HTTP request with assertions, and linking it to an endpoint is optional. If you do have a spec, schema assertions check every response against the contract.
Which assertions and auth schemes are supported?
Assertions cover status, headers, body, JSON paths, latency, and schema with ten operators, and requests chain by extracting values for later steps. Auth resolves per environment across ten schemes, from Bearer and API key to OAuth2, JWT, and AWS SigV4.
Can I run API tests in CI?
Yes. The CLI and the GitHub Action run suites with CI exit codes and JUnit or SARIF output, cron schedules run them unattended, API-key triggers start them from your own pipeline, and HMAC-signed webhooks report completion.
Does API testing include security scanning?
Yes. OWASP API Top 10 scans run beside the functional suites, with personas for multi-identity access testing, a triage workflow with an audit trail, and a security score.
One living spec
The rest of the lifecycle
Every stage below works from the same spec, so a change is made once and published once.
Ready to ship on it?
Routebase is live. Design your API once — docs, mocks, tests, and monitoring all follow from the same source.
14-day Pro trial — no credit card required.